
The India CISO Incident Response Playbook
PROACTIVE DATA SYSTEMS · AN OPERATIONAL PLAYBOOK FOR INDIAN ENTERPRISES
CERT-In and DPDP Ready in the First Six Hours
Four dimensions, five time targets, the 20 reportable categories, a severity matrix and a 90-day roadmap for passing the six-hour test
In briefUnder the CERT-In Directions of 28 April 2022, organisations in India must report any of 20 specified categories of cyber incident to CERT-In within six hours of noticing or being notified of them. It is the shortest mandatory reporting window of any major jurisdiction. The DPDP Rules, 2025 add a duty to intimate the Data Protection Board without delay and file a detailed report within 72 hours where personal data is involved. This playbook gives you a four-dimension readiness model (Signal Integrity, Classification Discipline, Escalation Certainty, Evidence Defensibility), five time targets from detection to submission, the 20 reportable categories, a severity matrix, an evidence standard, sector overlays for BFSI, manufacturing and IT/ITeS, a four-level scorecard and a 90-day roadmap. A CISO can score the organisation in an afternoon. |
Your CERT-In clock starts the moment you know, not when you are ready. The cost of a data breach in India averaged INR 220 million in 2025, up 13% from INR 195 million in 2024 (IBM Cost of a Data Breach Report, India segment). A late or badly documented CERT-In report adds regulatory exposure on top of that, and it is the part of a breach most within your control.
Most organisations we meet have an incident response policy. The question this playbook asks is different: has anyone tested whether the first six hours work at 11 pm on a Friday, with the CISO out of reach? In Proactive's readiness assessments, the most common answer is no. The policy exists on paper and has never been timed.
Proactive Data Systems, a Cisco Preferred Partner across all five architectures with 35 years in Indian enterprise infrastructure, has run six-hour readiness assessments and simulated drills for over 500 Indian enterprises since 2025. The time targets in this playbook are the targets we set and test in those engagements.
What Does a Missed Six-Hour Window Look Like?
It looks like a contained breach and an uncontained regulatory exposure. The scenario below is illustrative, a composite of patterns from incident reviews, not a single real case. Picture a mid-sized NBFC in Mumbai. On a Friday evening, a privileged account authenticates from an unfamiliar geography. The SIEM fires an alert, one of several hundred that shift. This is how the next six hours unfold without readiness.
|
08:40 pm Alert triggers. Analyst flags it for review. 09:55 pm True positive confirmed, but MFA logs are not centralised. Retrieval stalls for over an hour. 10:40 pm Legal is called. Debate begins on whether this is a CERT-In reportable incident. 11:20 pm Access to a customer data repository confirmed. Personal data is in scope. 12:15 am CISO is reached. Reporting ownership still being established. 02:50 am Initial report drafted. The six-hour window closed at 02:40 am. The breach itself was limited. The regulatory exposure came from delay, ambiguity and log retrieval gaps, not from the severity of the incident. |
Four structural failure patterns recur across BFSI, IT/ITeS and manufacturing. They are the predictable result of investing in detection technology without investing equally in the process and governance that turns a detection signal into a defensible regulatory response.
| Failure Pattern | What It Costs You |
|---|---|
| 1. Identity logs incomplete or inaccessible | Identity and MFA logs sit in several systems. Retrieval needs manual work. The 15 to 30 minute log retrieval target is missed in the first hour and every later step slips. |
| 2. Severity classification unclear | No pre-agreed severity matrix mapped to CERT-In categories. Teams debate reportability instead of executing it. Legal, which should validate, becomes a decision gate. |
| 3. Reporting ownership ambiguous | No named reporting officer. No out-of-hours rotation. The SOC assumes Legal will decide, Legal assumes the CISO will escalate, and the CISO is not on call. Weekend incidents go unreported. |
| 4. Evidence capture informal | Logs are overwritten during containment. Artefacts are not timestamped. When scrutiny arrives, the timeline is reconstructed from memory, not documented from the start. |
These are process and governance failures, not technology failures, and all four are fixable before an incident.
Who Is This Playbook For?
CISOs, CROs, legal counsel and security operations leaders accountable for CERT-In and DPDP compliance. It is an operational document, meant to be used on the day of an incident, not only read in preparation for one. Three reader groups will use it differently.
| Reader | Primary Focus | Read First |
|---|---|---|
| CISO / Head of Security | Framework ownership, readiness posture, board reporting | All sections |
| Legal Counsel / Compliance | CERT-In and DPDP obligations, regulatory grey areas, evidence chain | Regulatory Requirements; Governance and Board Exposure |
| SOC Lead / IR Manager | Detection benchmarks, severity matrix, evidence protocols | The First Six Hours Operating Model; Decision Models and Evidence Standards |
What Is the Six-Hour Assurance Model?
The Six-Hour Assurance Model is the readiness model Proactive uses to score CERT-In reporting capability on four dimensions: Signal Integrity, Classification Discipline, Escalation Certainty and Evidence Defensibility. The dimensions themselves are standard incident response (detect, classify, escalate, evidence). What the model adds is India-specific time targets for each one and a direct mapping to the CERT-In categories. Failure in any one dimension is enough to miss the window.
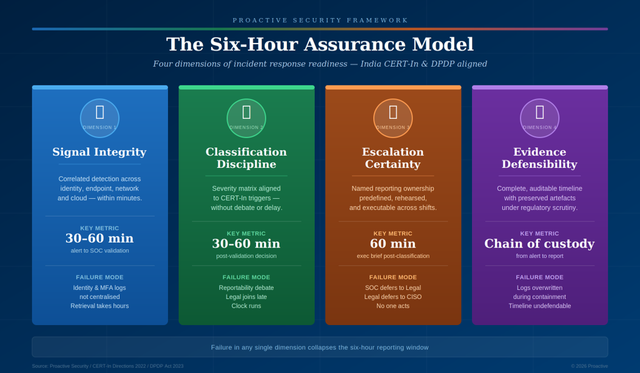
The Six-Hour Assurance Model: four dimensions of incident response readiness.
Dimension 1: Signal Integrity
Can you generate accurate, correlated detection signals across identity, endpoint, network and cloud within minutes of an anomalous event? Everything else depends on this. Without it, the other three dimensions do not matter because the incident is not yet known.
The usual failure is not a lack of tools. It is fragmented telemetry: identity logs in one place, endpoint logs in another, MFA records not centralised, cloud control plane events in a system separate from the on-premises SIEM. When retrieval takes several manual steps across several systems, the 30 to 60 minute validation target is out of reach.
Dimension 2: Classification Discipline
Can your team apply a severity matrix aligned to CERT-In triggers without debate or delay? Classification is separate from investigation. It answers one question: does this incident meet the threshold for regulatory reporting? That question must be answerable within 30 to 60 minutes of validation. If classification needs legal debate or senior approval every time, the process depends on who is available, not on agreed criteria. The matrix removes that dependency by fixing the criteria in advance.
Dimension 3: Escalation Certainty
Is reporting ownership predefined, rehearsed and workable across shifts? At any hour, on any day, there must be one named individual whose job is to authorise and submit the CERT-In notification. The failure mode is structural ambiguity: the SOC assumes Legal will decide, Legal assumes the CISO will escalate, the CISO is not on call. Ownership must be documented, tested and on a rotation.
Dimension 4: Evidence Defensibility
Can your team produce a complete, auditable incident timeline with preserved artefacts under regulatory scrutiny? This is the standard a CERT-In inspection or a later legal challenge will apply. The requirement is not a perfect investigation. It is disciplined documentation: every detection event, log retrieval, classification decision, escalation and submission carries a timestamp and an accountable name, with chain of custody kept from the moment of detection.
If you already run ISO 27035 or NIST CSF 2.0, the model sits on top as a CERT-In compliance layer: it maps to the ISO Detect and Assess phases and to the NIST Respond function, and adds the time targets and ownership rules neither prescribes.
The First Six Hours Operating Model
The operating model turns the four dimensions into a sequence of time-bound steps from detection to submission. Each step has a named owner and a time target. If either is missing, that is a gap to fix.
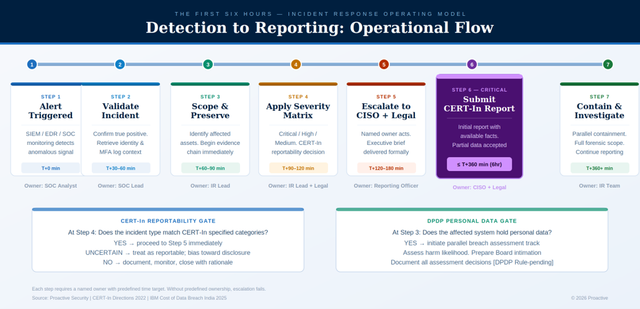
First six hours operational flow: detection to reporting, with regulatory decision gates.
What are the time targets for each step?
Five targets, from 30 to 60 minutes for detection-to-validation through to CERT-In submission within six hours of detection. These are the targets Proactive sets and tests in readiness engagements. They are not legal thresholds and not measured industry medians; they are what we have found an organisation needs to hit, with margin, to submit inside six hours under normal conditions. High-risk sectors and complex log environments should aim for the lower end of each range.
| Step | Target Time | Owner Role | Critical Dependency |
|---|---|---|---|
| Detection to SOC validation | 30 to 60 minutes | SOC Analyst / Lead | Centralised identity and MFA logs |
| Log retrieval for critical systems | 15 to 30 minutes | SOC Lead | SIEM configuration and retention policy |
| Severity and reportability decision | 30 to 60 min after validation | IR Lead + Legal | Pre-agreed severity matrix |
| Executive brief delivery | Within 60 min of classification | Reporting Officer | Named owner with out-of-hours access |
| CERT-In initial submission | Within 6 hours of detection | CISO / Legal | Pre-built report template, minimum viable dataset |
If you cannot measure these five intervals today, your six-hour readiness is assumed, not confirmed.
How does six hours compare with other jurisdictions?
It is the shortest mandatory cyber incident reporting window among major jurisdictions. The EU gives 72 hours, Singapore three days, the US four business days for listed companies, and Australia 30 days to assess.
| Jurisdiction and Regime | Window | Reported To |
|---|---|---|
| India, CERT-In Directions 2022 | 6 hours from noticing or being notified | CERT-In |
| India, DPDP Rules 2025 (personal data) | India, DPDP Rules 2025 (personal data) | Data Protection Board and affected individuals |
| European Union, GDPR Article 33 | 72 hours from awareness | Supervisory authority |
| Singapore, PDPA | 3 calendar days from assessment | PDPC |
| United States, SEC Form 8-K (listed companies) | 4 business days from materiality determination | SEC, public filing |
| Australia, Notifiable Data Breaches scheme | Assess within 30 days; notify as soon as practicable | OAIC |
Windows are as published by each regulator at the time of writing and are triggered by different events (awareness, assessment, materiality). Confirm the current text before relying on any of them.
What Do CERT-In and DPDP Actually Require You to Do?
CERT-In requires an initial report within six hours of detection or awareness, whichever is earlier. DPDP requires breach intimation to the Data Protection Board without delay, a detailed report within 72 hours, and notice to affected individuals without delay. Regulatory text describes obligations; this section turns them into operational actions. CISOs and Legal should review it together.
CERT-In: the six-hour reporting obligation
Under the CERT-In Directions of 28 April 2022, issued under Section 70B(6) of the IT Act, 2000, the six-hour clock creates four operational requirements, plus two standing ones.
- Detect and validate incidents continuously, across all material systems.
- Decide reportability quickly, on pre-agreed criteria, not in-flight deliberation.
- Submit an initial report with available facts. Completeness is not required at T+6 hours. Submission is.
- Preserve a defensible evidence trail from the moment of detection.
- Standing: keep logs of all ICT systems for a rolling 180 days, within Indian jurisdiction.
- Standing: synchronise system clocks to the NIC or NPL NTP servers, or servers traceable to them.
Which incidents must be reported to CERT-In?
Twenty categories, listed in Annexure I of the Directions. Any incident in one of them is reportable within six hours, whatever its scale. Map your severity matrix to this list, not to a generic one.
| S.No | Reportable incident category (Annexure I, CERT-In Directions 2022) |
|---|---|
| 1 | Targeted scanning or probing of critical networks or systems |
| 2 | Compromise of critical systems or information |
| 3 | Unauthorised access of IT systems or data |
| 4 | Website defacement or intrusion, including injected malicious code or links |
| 5 | Malicious code attacks: virus, worm, Trojan, bots, spyware, ransomware, cryptominers |
| 6 | Attacks on servers (database, mail, DNS) and network devices (routers) |
| 7 | Identity theft, spoofing and phishing attacks |
| 8 | Denial of Service and Distributed Denial of Service attacks |
| 9 | Attacks on critical infrastructure, SCADA, OT systems and wireless networks |
| 10 | Attacks on applications such as e-governance and e-commerce |
| 11 | Data breach |
| 12 | Data leak |
| 13 | Attacks on IoT devices and associated systems, networks, software and servers |
| 14 | Attacks or incidents affecting digital payment systems |
| 15 | Attacks through malicious mobile apps |
| 16 | Fake mobile apps |
| 17 | Unauthorised access to social media accounts |
| 18 | Attacks or malicious or suspicious activity affecting cloud computing systems, servers, software or applications |
| 19 | Attacks or suspicious activity affecting big data, blockchain, virtual assets and exchanges, custodian wallets, robotics, 3D/4D printing, additive manufacturing or drones |
| 20 | Attacks or suspicious activity affecting AI and machine learning systems |
Wording condensed from Annexure I. Use the official text in your severity matrix.
How do you submit a CERT-In report?
By email to [email protected], by phone on 1800-11-4949 or fax on 1800-11-6969, using the incident reporting format published on cert-in.org.in. Pre-fill the format with your organisation details and keep it, with the minimum viable dataset fields blank, in the reporting officer's offline kit. Nobody should be opening the format for the first time at 2 am.
Four grey areas to interpret before an incident
| Grey Area | The Question | Safeguard |
|---|---|---|
| What counts as "awareness"? | If an alert fires but is not yet validated, does the clock start at signal time or confirmation time? | Record both timestamps. Track alert-to-validation intervals. Whichever interpretation prevails, you can show diligence. |
| Third-party notification | If a vendor tells you of a compromise affecting your systems, when does the clock start? | Treat it as starting at notification. Put immediate breach-notification and evidence-sharing clauses in every vendor contract. |
| Partial facts at reporting time | Is it acceptable to report before the picture is complete? | Yes. CERT-In permits reporting with available information. Define a minimum viable reporting dataset in advance so nobody hesitates. |
| Internal debate | Must Legal sign off before submission? | Our position: Legal validates, it does not decide. The severity matrix fixes reportability thresholds beforehand, with Legal's agreement, so the 2 am decision is execution, not deliberation. |
DPDP Act, 2023 and Rules, 2025: personal data breach obligations
The DPDP Rules were notified on 13 November 2025. For a personal data breach, a Data Fiduciary must intimate the Data Protection Board without delay, follow with a detailed report within 72 hours of becoming aware (extendable on written request), and notify each affected Data Principal without delay, in plain language, covering what happened, the likely consequences, what has been done and what they should do. The breach provisions come into force on a phased timetable, 18 months after notification. Treat them as the operating standard now; the drill you run in 2026 is the one you will be judged on in 2027.
In operational terms, DPDP creates five requirements.
-
Confirm personal data presence in affected systems within the initial scope assessment.
-
Determine evidence of access, disclosure, alteration, loss or exfiltration.
-
Assess the likelihood of harm to affected Data Principals.
-
Prepare Board and Data Principal notifications from pre-approved templates.
-
Document every assessment decision with a timestamp and a named decision-maker.
CERT-In tests speed. DPDP tests judgement and documentation. Evidence Defensibility is the common foundation for both.
What if you miss the six-hour window?
Report anyway, immediately, and document why you were late. A late report with a timestamped rationale is defensible; silence is not. Non-compliance with the Directions is punishable under Section 70B(7) of the IT Act, 2000, with imprisonment of up to one year, a fine of up to one lakh rupees, or both, and the reputational cost of a public enforcement action is larger than the fine. Three things to do in the first hour after you realise the window has passed.
-
Submit what you have to [email protected] now, marked as an initial report, with the detection and awareness timestamps stated.
-
Write the delay rationale into the incident timeline while it is fresh: which step overran, why, and who decided what.
-
Brief the CISO and Legal that the late submission itself is now a board-reportable event, and schedule the post-incident review within 30 days.
This playbook is general guidance, not legal advice. Confirm your specific obligations under the CERT-In Directions and the DPDP Act and Rules with qualified counsel, and have counsel track the phased DPDP commencement dates.
How Do You Decide Whether an Incident Is Reportable?
In five steps, using a pre-agreed severity matrix, with a bias towards reporting when indicators are credible and systems are critical. This is the one-page logic your SOC should be able to run at 2 am without escalating to Legal.
| Decision Step | Action Required |
|---|---|
| 1. Confirm validated incident | True positive confirmed. Not a false alarm. |
| 2. Map to CERT-In categories | Does the incident type appear in CERT-In's specified list? Apply the severity matrix. |
| 3. Capture minimum viable facts | Affected systems, initial timeline, estimated scope, incident type. Completeness is not required. |
| 4. Submit initial report within 6 hours | Report when indicators are credible and systems are critical. Do not wait. |
| 5. Schedule follow-up updates | CERT-In expects updates as the investigation progresses. Build the cadence into the IR plan. |
Severity and regulatory linkage matrix
| Severity | Operational Definition | CERT-In Action | DPDP Action |
|---|---|---|---|
| Critical | Confirmed compromise, business disruption, ransomware, or data breach confirmed | Treat as reportable. Submit within 6 hours. | Intimate the Board without delay; start the 72-hour detailed report; notify affected individuals |
| High | Confirmed intrusion or unauthorised access, partial containment | Assess reportability. Escalate immediately. | Assess personal data exposure scope |
| Medium | Credible suspicious activity, no confirmed impact | Monitor. Escalate if the situation worsens. | Assess if personal data systems are in scope |
| Low | Isolated event, no business or data impact confirmed | Document and close with rationale. | Not applicable |
Customise this matrix to your risk profile, sector and data architecture. Version-control it and re-validate it at least annually or after any significant regulatory change.
What evidence must you capture, and by when?
Seven artefact categories, captured from T+0 to T+90 minutes, with a dedicated evidence custodian from the first hour. Your regulatory defence rests on this chain. Evidence is captured from the moment of detection, not reconstructed after containment.
| Evidence Category | Specific Artefacts | Capture Priority |
|---|---|---|
| Detection record | Alert identifier, SIEM correlation ID, first-seen timestamp | Immediate at T+0 |
| Identity events | Authentication logs, MFA records, privileged access activity, role changes | Within 30 minutes |
| Affected asset inventory | Hostnames, IPs, cloud resource IDs, system classification | Within 30 minutes |
| Endpoint artefacts | Process execution logs, lateral movement indicators, persistence mechanisms | Within 60 minutes |
| Network and DNS logs | Connection logs, DNS queries, data transfer volume indicators | Within 60 minutes |
| Cloud control plane | API calls, configuration changes, IAM events | Within 60 minutes |
| Data access logs | File access, database query logs, exfiltration indicators where applicable | Within 90 minutes |
Keep one authoritative incident timeline. Record who captured what, and when. Containment must not overwrite or modify evidence sources.
What does detection delay cost?
On the IBM India 2025 baseline of INR 220 million, Proactive's planning assumption of a 10 to 15% cost escalation from delayed containment is INR 22 to 33 million per incident. The 10 to 15% is our assumption for budgeting, not a measured finding; IBM's global reports consistently show breaches with longer lifecycles costing more, and this range is a conservative reading of that pattern for planning purposes. Figure 3 models the bands.
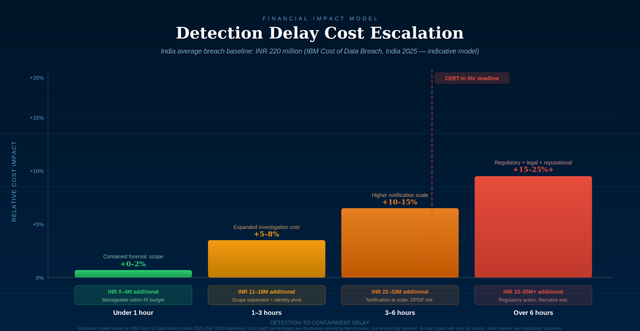
Detection delay cost escalation, an indicative model on the IBM India 2025 baseline of INR 220 million.
The bands are planning benchmarks, not empirical findings. They exist to quantify the case for investing in detection latency reduction. Actual impact varies by sector, incident type, data volume and regulatory outcome. Calibrate against your own breach cost assumptions.
How Does the Model Apply to BFSI, Manufacturing and IT/ITeS?
The four dimensions apply everywhere. The priorities differ by sector. BFSI faces multiple regulators at once, manufacturing faces IT/OT scope problems, and IT/ITeS faces client contract deadlines that can be shorter than CERT-In's. Treat these overlays as starting points for your own calibration.
Banking, Financial Services and Insurance
|
Illustrative scenario. A private bank's internet banking platform suffers a credential-stuffing attack on 4,200 accounts, detected by anomaly scoring at 11:15 pm on a Friday. The CISO is not in office. The SOC lead cannot confirm who the after-hours CERT-In reporting officer is. Without readiness: the incident is not formally escalated until Saturday morning. The window passes. The bank faces scrutiny for the reporting delay more than for the breach. With readiness: the rotation names a deputy reporting officer. The severity matrix classifies the event as Critical on account volume. The CERT-In submission is filed by 04:45 am with available facts. |
BFSI organisations answer to several regulators at once. CERT-In's obligation sits alongside RBI's cybersecurity framework for banks and NBFCs, SEBI's cyber resilience framework for market participants and IRDAI's guidelines for insurers. They share principles but differ in timelines and formats.
-
Align the CERT-In severity matrix with RBI, SEBI and IRDAI obligations. One incident may need several notifications, in sequence or in parallel.
-
Bring fraud operations into the first-six-hour workflow. Fraud indicators often precede or accompany identity-based breaches.
-
Aim for the lower end of every detection benchmark. Board scrutiny in BFSI is immediate.
-
Keep regulator-ready evidence in separate log repositories that containment actions cannot modify.
Manufacturing and Industrial
|
Illustrative scenario: A precision engineering firm in Pune detects lateral movement from an IT segment towards an OT-connected system. The vector is a vendor remote access session left open after a maintenance window. Challenge: OT systems do not produce standard SIEM-compatible logs. The IR Lead cannot tell whether the OT network was reached. Scope validation stalls. Readiness requirement: OT visibility in the detection architecture, vendor access auto-revoked at session timeout, and a separate OT scope assessment runbook. |
IT/OT convergence creates scope validation problems that can consume the whole six-hour window. A detection architecture that covers only IT is incomplete for this sector.
-
Include OT log visibility in the readiness scope. If OT telemetry cannot be queried within 30 minutes, that is a Signal Integrity gap.
-
Validate IT/OT segmentation as a live control, with penetration tests of the boundary in every readiness exercise.
-
Give vendor access governance an immediate revocation capability. Third-party access is a primary breach vector in manufacturing.
-
Protect plant-level configuration backups as incident evidence. They are frequently overwritten during recovery.
Information Technology and IT-Enabled Services
|
Illustrative scenario. A mid-sized IT services firm finds that a client-dedicated cloud environment was accessed with a compromised developer credential. The client's production data is affected. The firm's CERT-In duty is clear; the client's contractual notification deadline is separate and possibly shorter. Compounding factor: a distributed remote workforce. The identity event came from an overseas IP. Deciding whether it was a legitimate remote employee or a threat actor with stolen credentials takes extra time. Readiness requirement: cloud control plane logs centralised and queryable in real time; client notification obligations pre-mapped into the escalation workflow. |
For IT/ITeS, contractual exposure to clients can match or exceed regulatory exposure. The operating model has to satisfy CERT-In and client notification timelines at the same time.
-
Centralise cloud control plane and SaaS logs into the primary SIEM. Cloud is the main attack surface for this sector.
-
Map client contractual notification obligations before an incident. Some enterprise contracts require notice within two to four hours.
-
Treat remote workforce identity risk as a continuous, elevated-priority signal.
-
Write client communication templates in advance. Drafting them during an incident costs time you do not have.
What Will the Board Ask After an Incident?
Three questions: was reporting timely, was decision-making documented, and was evidence preserved? Regulators and auditors examine the same three. Incident response maturity is a governance issue, not only a technical one, and DPDP's governance provisions put directors within reach of scrutiny when documentation is weak.
| Board Question | What Regulators and Auditors Examine |
|---|---|
| Was reporting timely? | Timestamps from detection to submission. Any gap beyond six hours needs a documented rationale. |
| Was decision-making documented? | Written records of classification decisions, reportability assessments and escalation actions, with named decision-makers. |
| Was evidence preserved? | Chain of custody from detection through reporting. Its absence is an audit vulnerability. |
Governance Safeguards
-
Board-approved incident reporting owner, documented and reviewed annually.
-
Quarterly readiness score presented to the Audit or Risk Committee, using the four Assurance Model dimensions.
-
Tabletop exercises minuted and available for regulator review.
-
Post-incident review reports shared with the Audit Committee within 30 days of closure.
-
Legal counsel briefed on CERT-In and DPDP before an incident, not during one.
Where Does Your Organisation Sit? The Readiness Scorecard
In Proactive's readiness assessments, the most common starting point is Level 2: processes exist on paper and have not been timed. Score each of the four dimensions quarterly on the scale below. The IR Lead scores, in consultation with Legal, and presents to the CISO and Audit Committee. The gap between Level 2 and Level 3 is a process and rehearsal investment, not a technology one.
| Maturity Level | Definition |
|---|---|
| Level 1: Absent | The dimension has not been assessed. No defined processes or ownership exist. |
| Level 2: Developing | Processes exist in documentation but have not been tested operationally. |
| Level 3: Tested | Processes have been tested in tabletop exercises and the team can meet the benchmarks under controlled conditions. |
| Level 4: Board-Tested | Processes have been tested in full simulation, results presented to the board, and identified gaps closed. |
| Dimension | Level 3 Indicators | Level 4 Indicators |
|---|---|---|
| Signal Integrity | All log sources centralised and queryable. Retrieval benchmark met in tabletop. | Live simulation confirms retrieval within 15 to 30 min. Gap analysis presented to board. |
| Classification Discipline | Severity matrix documented and rehearsed. Legal aligned on thresholds. | Matrix tested in full simulation. Results reviewed by Audit Committee. |
| Escalation Certainty | Named reporting owner documented. Out-of-hours rotation in place. | Rotation tested out of hours. Board knows the named owner and deputy. |
| Evidence Defensibility | Artefact capture protocol defined. Evidence custodian assigned. | Chain of custody tested in simulation. Board shown an example timeline. |
If you cannot place your organisation at Level 3 on all four dimensions, your six-hour window is at risk. The roadmap below is built to get you there in 90 days.
How Do You Reach Level 3 in 90 Days?
In three phases: fix ownership, the matrix and the log inventory in days 1 to 30; build runbooks, the DPDP checklist and the first tabletop in days 31 to 60; run a full timed simulation and present it to the Audit Committee in days 61 to 90. Each activity has an owner and maps to an Assurance Model dimension. Organisations with an existing IR programme should use this as a gap assessment, not a from-scratch build.
| Phase | Activity | Owner | Dimension |
|---|---|---|---|
| Days 1 to 30 | Confirm and document reporting ownership. Name deputy and out-of-hours rotation. | CISO + Legal | Escalation Certainty |
| Days 1 to 30 | Finalise severity matrix mapped to CERT-In categories. Align with Legal. | IR Lead + Legal | Classification Discipline |
| Days 1 to 30 | Audit log inventory. Identify retrieval gaps. Set remediation targets. | SOC Lead | Signal Integrity |
| Days 1 to 30 | Define minimum viable CERT-In reporting dataset. Build submission template. | Legal + IR Lead | Escalation Certainty |
| Days 31 to 60 | Deploy runbooks for the five most likely scenarios: ransomware, privileged credential compromise, data exfiltration, vendor remote-access compromise, cloud control plane compromise. | IR Lead | All |
| Days 31 to 60 | Finalise DPDP assessment checklist and personal data scope map. | Legal + Privacy Lead | Evidence Defensibility |
| Days 31 to 60 | Run a cross-functional tabletop on one realistic scenario. | CISO | All |
| Days 31 to 60 | Define evidence custodian role and artefact capture protocol. | IR Lead | Evidence Defensibility |
| Days 61 to 90 | Run a full simulation from detection to CERT-In submission. Time each step. | CISO + IR Lead | All |
| Days 61 to 90 | Measure results against benchmarks. Score against the maturity model. | IR Lead + Legal | All |
| Days 61 to 90 | Present simulation results to the Audit Committee. | CISO | All |
| Days 61 to 90 | Close identified gaps. Update runbooks and matrix. | IR Lead | Dimension-specific |
What should you be able to prove at day 90?
Six outcomes. Use them as acceptance criteria.
-
Detection-to-escalation under two hours, tested under simulation.
-
Named reporting officer with documented deputy and out-of-hours rotation.
-
Critical log retrieval under 30 minutes, verified by rehearsal.
-
Severity matrix applied without Legal debate in a tabletop exercise.
-
CERT-In initial submission template pre-populated and approved.
-
Simulation results documented and presented to the Audit Committee.
If you cannot show these six, readiness is still assumed, not confirmed.
Which Controls Shorten the First Six Hours?
Six control domains, led by centralised identity logging and unified XDR telemetry, because every dominant breach vector targets identity first. Controls must compress response time and reduce ambiguity. The table maps each to its operational benefit, its reporting benefit and the dimension it strengthens. Use it to prioritise technology investment where readiness is the objective.
| Control Domain | Operational Benefit | Reporting Benefit | Dimension |
|---|---|---|---|
| Phishing-resistant MFA (e.g. FIDO2) | Fewer credential-based incident triggers | Fewer reportable identity incidents overall | Signal Integrity |
| Centralised identity and access log platform | Faster scope validation. MFA logs queryable within minutes. | Reportability decisions backed by log evidence | Signal Integrity |
| Policy-based network segmentation | Limits lateral movement after compromise. Contains blast radius. | Less scope uncertainty in the submission | Classification Discipline |
| Unified SIEM / XDR platform | Correlated alerts across identity, endpoint, cloud. Fewer false positives. | Fast, defensible timeline reconstruction | Signal Integrity + Evidence Defensibility |
| Vendor access governance platform | Immediate revocation of third-party sessions on alert | Clear third-party responsibility in the report | Escalation Certainty |
| Cloud control plane monitoring | Real-time visibility of API and IAM events | Complete cloud-scope evidence for CERT-In | Signal Integrity + Evidence Defensibility |
Architecture decides whether six-hour readiness is achievable or permanently aspirational. An organisation with fragmented log infrastructure cannot meet the Signal Integrity benchmarks however much process it adds. Both are needed. Verizon's 2025 DBIR identifies credential abuse, token replay in cloud control planes, privileged account exploitation and vendor trust abuse as the dominant breach vectors globally, and finds around 68% of breaches involve the human element. Verizon does not publish an India breakdown. A detection architecture without identity telemetry as a primary signal will keep missing the early stages of these attacks.
Six Hours, Engineered
Six hours is a test of four things at once: the quality of your detection signals, the clarity of your decision criteria, the discipline of your governance and the strength of your evidence chain. Most Indian enterprises have invested in detection technology. Fewer have tested whether process and governance can turn a signal into a defensible CERT-In submission inside the window. Fewer still have measured that under realistic conditions and shown the board the result. Readiness is a demonstrated, time-stamped, board-reviewed capability, not a posture.
Proactive Data Systems, a Cisco Preferred Partner across all five architectures with 35 years in Indian enterprise infrastructure, helps Indian enterprises engineer the first six hours. We design and deploy identity, access, segmentation and detection architectures on Cisco Duo, Cisco ISE, Cisco Secure Access and Cisco XDR, then test them under realistic incident conditions. Every engagement ends with a scored assessment against the Six-Hour Assurance Model, a quantified gap report, a 90-day remediation plan and a simulated six-hour drill with documented results.
Want to know your level? Ask Proactive for a six-hour readiness assessment. We will score your four dimensions, run the drill, and give you the evidence for your next Audit Committee meeting.
(Request a Six-Hour Readiness Assessment)
Sources
-
CERT-In Directions under Section 70B(6) of the IT Act, 2000, dated 28 April 2022, including Annexure I, and associated FAQs. Ministry of Electronics and Information Technology, Government of India.
-
Information Technology Act, 2000, Section 70B(7).
-
GDPR Article 33; Singapore PDPA Part 6A; US SEC Form 8-K Item 1.05; Australia Privacy Act 1988 Part IIIC.
-
Digital Personal Data Protection Act, 2023, and Digital Personal Data Protection Rules, 2025 (notified 13 November 2025). Government of India.
-
IBM Security. Cost of a Data Breach Report 2024 and 2025, India segment data.
-
Verizon. Data Breach Investigations Report 2025.
-
ISO/IEC 27035-1:2023, Information security incident management.
-
NIST Cybersecurity Framework 2.0.
Figures are drawn from published research and vary by source, methodology and year. Verizon does not publish an India breakdown; global figures are cited as directional context. Verify current data before citing externally.
Frequently Asked Questions
What is the CERT-In six-hour reporting rule?
When does the CERT-In clock start?
What does DPDP require after a personal data breach?
Which incidents must be reported to CERT-In?
What is the penalty for not reporting to CERT-In?
What is the Six-Hour Assurance Model?
How long does it take to become six-hour ready?
Want this as a document you can share internally?
Download PDF