Updated: 12 November 2026
Managed networks for Indian BFSI branches cover core banking availability, ATM and self-service resilience, RBI cybersecurity directive alignment, DPDP Rule 6 evidence, CERT-In six-hour incident reporting readiness, and PSTN handoff for branch calling. Delivered on Cisco Meraki with Cisco Secure Firewall by a Cisco Penta-Preferred Partner under the Cisco 360 Partner Program.
Written for BFSI CIOs, Heads of Retail Banking IT, Chief Risk Officers, CISOs and Heads of Branch Operations at Indian scheduled commercial banks, small finance banks, NBFCs, cooperative banks, insurance companies and capital-markets entities.
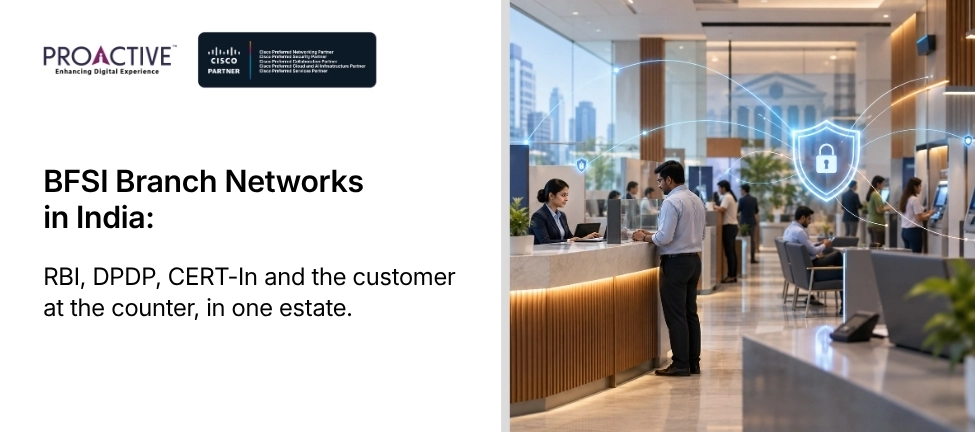
Walk into an Indian bank branch at 11 AM on a Wednesday and observe the density of regulated activity moving across the network in any given ten-minute window.
A relationship manager pulls a customer's account for a service request. The screen touches core banking, KYC records, transaction history, and product eligibility flags. Every one of those touches is logged for RBI audit and for internal audit. A teller processes a cash deposit. The transaction reaches core, updates the ledger, triggers an SMS to the customer, and prints a receipt. The customer's mobile number is personal data; DPDP applies. A card is presented at the counter for a linked account operation. PCI DSS applies to the cardholder data environment carrying that transaction. A new-account opening runs across CKYC servers hosted centrally; the network path carries KYC documents subject to specific retention and access rules.
Somewhere in the branch, an ATM services a customer whose card fails at the acquirer. Somewhere else, a self-service kiosk times out mid-loan-application because the WAN link degrades. Three floors up in the corporate office, the CERT-In reporting analyst is watching for anything that looks like the kind of incident that starts the six-hour clock.
No other Indian enterprise sector runs this many regulators through a single physical estate in a single working hour. BFSI branch networks are, structurally, the most heavily supervised production networks in the country. Managed networks in BFSI exist to make that supervision routine rather than existential.
Four RBI expectations sit on top of a modern bank branch network.
Cyber Security Framework compliance. The 2016 Cyber Security Framework for Banks, subsequently updated through the RBI’s Cyber Resilience and Digital Payment Security Controls directions, requires banks to have an IT and cyber security framework proportionate to their risk profile. Network operations sit inside this: segmentation between customer-facing and corporate systems, VAPT on critical systems periodically, incident reporting into the RBI’s monitoring channels, and IT outsourcing governance where a third party runs any part of the estate.
Data localisation for payment system data. The RBI’s April 2018 directive requires that all data related to payment systems operated in India must be stored only in India. Branches that carry payment data traffic (which is all of them) must terminate that traffic within India, on infrastructure that satisfies the localisation requirement. Cross-border replication is permitted only for specific processing scenarios, with the data returned and stored onshore.
Business continuity and disaster recovery. RBI expects banks to demonstrate ability to recover critical systems within defined windows. Branch networks are the delivery layer for that recovery; if the network cannot switch over to the DR path, the DR itself does not deliver.
Outsourcing governance. When a bank uses a managed services partner, RBI’s outsourcing framework applies: due diligence on the vendor, defined SLAs, right to audit, exit provisions, and reporting. A managed contract that satisfies RBI’s outsourcing expectations comes with contract clauses that address each of these explicitly.
An Indian bank running its branch network under a managed contract on Cisco Meraki with Cisco Secure Firewall, delivered by a Cisco Penta-Preferred partner with Services Preferred designation, is meeting the operational substance of these expectations. The evidence side (documentation, audit trails, reporting) is produced by the managed operator's normal reporting cadence.
A bank branch network carries five categories of critical traffic.
Core banking. The teller and RM screens live and die by core reachability. When core is slow, the queue at the counter grows. When core is unreachable, the branch effectively stops. In many mid-sized Indian banks, one core outage will make it into the RBI's monthly reporting.
ATMs and self-service. Cash recyclers, deposit machines, statement kiosks, cheque deposit machines. Each has its own connectivity dependency. Consolidated failure of ATMs across a region triggers customer complaints, media attention and possible RBI inquiry.
Card acquirer path. The path from the branch POS or ATM to the acquirer processor. Failures on this path show up as declined transactions, which are the single most visible symptom of a network issue for the customer.
CKYC and back-office system connectivity. New account opening, loan processing, updates to customer records. Availability impacts branch productivity and customer wait times.
Voice and branch calling. Landlines for customer service, phones for RM outreach, connectivity for customer helplines routed through the branch. Increasingly, cloud calling with local PSTN handoff.
A well-run managed contract prioritises these five categories in the monitoring and alerting stack, applies path redundancy where the risk warrants, and treats degradation on any of them as a P1 or P2 incident with the corresponding SLA response.
DPDP Rule 6 requires reasonable security safeguards including encryption at rest and in transit, access limited to authorised persons, audit logs retained for a minimum of one year, and demonstrable ability to detect and reconstruct incidents. For BFSI, DPDP overlays existing RBI expectations rather than replacing them; where the two touch the same control, the stricter interpretation governs.
The single most common gap we find in Indian bank branch estates is the Cisco Secure Firewall rulebase. Rules accumulate over years of branch openings, product launches, temporary vendor access grants, and RM-request escalations. Nobody documents them consistently. On audit day, the DPO cannot demonstrate to the auditor that access is actually limited to authorised persons, because the rulebase has grown into a shape that even the security team does not fully understand.
Managed Firewall Services attack this directly. Every rule has a stated purpose, an owner, a review date and a documented change history. Every proposed change ships with a rollback path. The rulebase is curated, not accumulated. On DPDP audit day, the DPO shows a live register with dated entries, and the auditor moves to the next question.
CERT-In's 2022 Direction requires reporting of specified cyber incidents within six hours of the enterprise becoming aware. For a BFSI enterprise, the clock does not care whether the incident originated at head office or at branch 247 in a Tier-3 city.
Two operational needs follow. Detection has to happen at the branch, not only at the SOC in head office. Reporting has to be pre-wired so that the six-hour clock, once triggered, feeds into a defined workflow that reaches CERT-In, RBI (where applicable) and the DPDP Data Protection Board (where personal data is involved) in parallel.
Managed contracts in BFSI typically bake this into the runbook. Branch-level detection through the managed NOC. Automatic incident classification against CERT-In categories. Escalation to the customer's CISO within the first hour, with the reporting draft prepared for CISO review inside the third. The six-hour clock is a compressed workflow, not a scramble.
Branch calling (landlines for customer service, helpline connectivity, insurance-selling outreach, telephony for RM teams) is moving from legacy PBX to cloud calling in most Indian BFSI estates. The RBI does not directly regulate branch voice, but the DoT does regulate cloud calling: any Webex Calling or equivalent deployment in India must terminate PSTN through a DoT-licensed carrier, with call recordings and CDRs stored onshore.
For a BFSI branch running Webex Calling, this typically means Local Gateway at the branch or Cloud Connected Partner PSTN through Bharti Airtel or Tata Communications, plus call-recording retention aligned to RBI's own recording expectations for customer-service voice (typically seven years for regulated categories). Managed contracts handle the LGW versus CCPP decision per site and the retention configuration once.
Payment system data localisation is the RBI expectation that most often catches enterprises by surprise when they consider cloud-first services. The requirement is unambiguous: payment data storage in India. Processing may occur abroad, but the data must be returned and stored onshore.
For a managed network, this shapes several decisions. Log aggregation for payment-related network traffic must land in India-hosted SIEM instances. Backup and DR for firewall and network device configurations must sit onshore. Any cloud-managed dashboard capturing payment-related metadata must respect the localisation boundary. On Cisco Meraki, dashboard data hosting can be configured against India-region requirements; on Cisco Secure Firewall, log destinations are enterprise-controlled and readily aligned to localisation. Managed contracts document the localisation posture as part of the standard reporting package.
BFSI branch expansion runs at a specific rhythm. Regulatory approvals for branch openings, RBI reporting cycles, and internal risk clearance for each new site create a slower cadence than retail or QSR expansion. What matters is not raw rollout speed; it is that the site is fully compliant on the day it opens.
Managed contracts on Meraki templates deliver this. Each branch profile (metro, urban, semi-urban, rural, currency chest, wealth centre) has a locked configuration template that includes core banking VLAN definitions, ATM segment isolation, DPDP-scoped logging targets, RBI-aligned firewall policy, and branch voice configuration. A new branch, when hardware arrives, provisions itself against the template. Zero drift from Day 1.
BFSI CIOs typically face specific commercial preferences shaped by parent capital rules and audit committee posture.
CapEx is the historical default at most Indian banks. Hardware on the books, depreciated, refreshed on a rolling schedule. Suits banks with settled capital plans and audit committee preference for asset ownership.
OPEX is growing at growth-stage banks (small finance banks, digital-first NBFCs, insurers scaling distribution). Per-branch subscription pricing simplifies expansion planning. Refresh handled inside the term. Care needed with Ind AS 116 lease-accounting classification.
Managed-Only suits banks with a recently refreshed Meraki estate that want operational specialist attention without changing the asset side.
BFSI enterprises frequently mix models: OPEX for new branch openings and expansion, CapEx at flagship metro branches where the audit committee prefers ownership, Managed-Only for the stable corporate estate. Full walkthrough sits in the CapEx or OPEX decision guide.
Two days at your primary regional office, with your CIO, CISO, Head of Retail Banking IT and, ideally, Chief Risk Officer or DPO. We take a snapshot of the branch network estate, map it against RBI cybersecurity directives, DPDP Rule 6, CERT-In readiness and data localisation posture, walk the Cisco Secure Firewall rulebase for audit hygiene, and hand you a written finding by end of week.
Disclaimer: Regulatory references (RBI Cyber Security Framework for Banks, RBI Data Localisation Directive, DPDP Act and Rules, CERT-In Direction 2022) in this piece are drawn from currently published guidance and are for operational orientation, not regulatory or legal advice. Compliance posture for any specific BFSI enterprise depends on entity classification, product scope, audit outcome and RBI interpretation. A qualified regulatory adviser, chartered accountant or legal counsel is the definitive voice on BFSI compliance obligations.
We'll get back to you shortly.